Set the permitted scope.
AI availability, approved providers, and managed credential references belong to the organisation.
Security & AI
Set the scope for optional AI assistance. Keep source figures, reporting responsibilities, and professional judgment within a defined control model.
Organisation controls
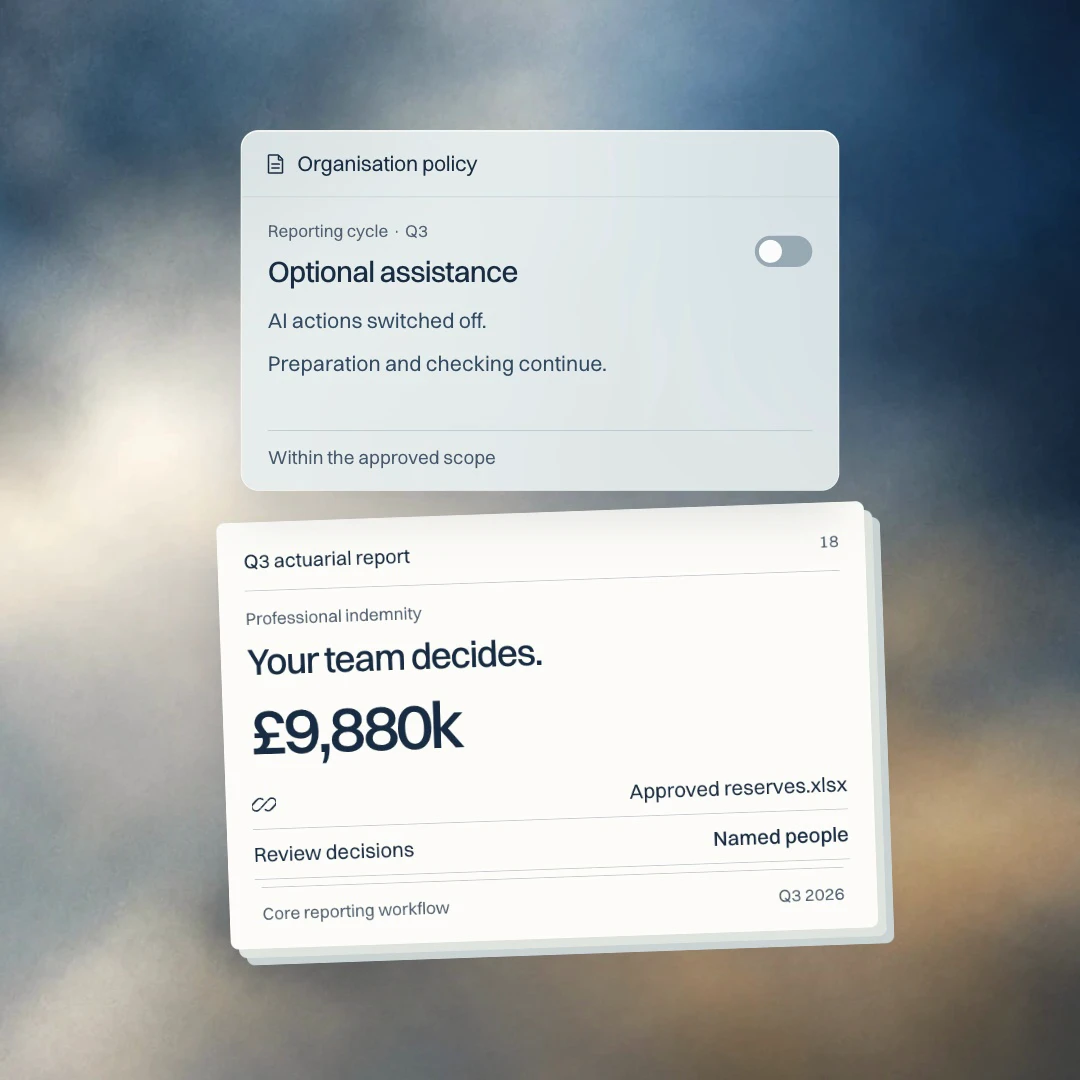
AI availability and provider configuration are organisation decisions. Each cycle and action operates within that approved scope.
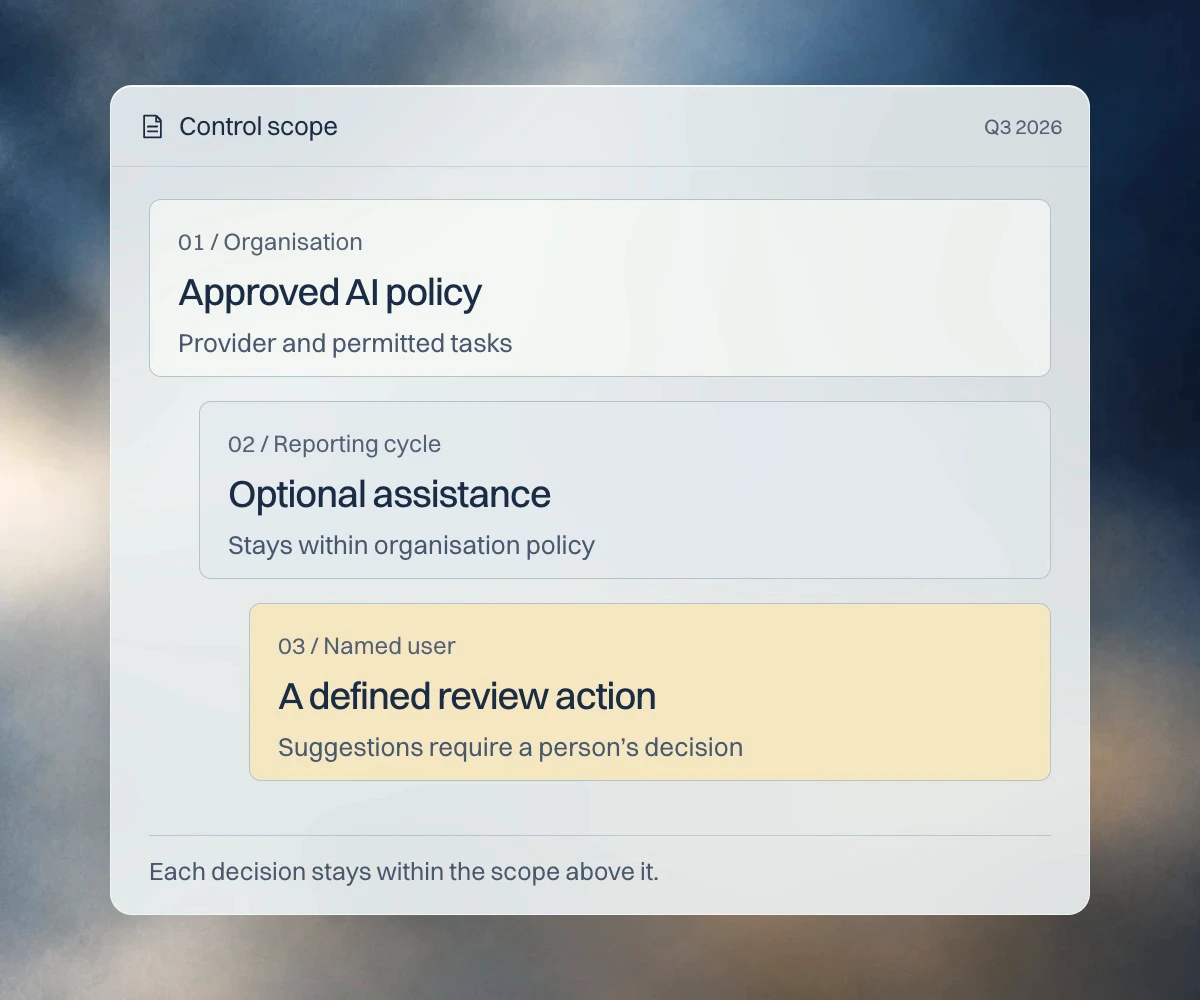
AI availability, approved providers, and managed credential references belong to the organisation.
A separate cycle setting can switch AI actions off. It cannot expand the organisation’s approved scope.
AI suggestions need a user decision. AI cannot calculate figures, approve work, or advance a review state.
Before an AI request
Approved mapping, statement-review, and wording tasks pass through a bounded gateway. Extra tools, messages, or endpoint changes are rejected.
The documented policy masks supported figure formats. A bounded gateway validates the allowed task before transport.
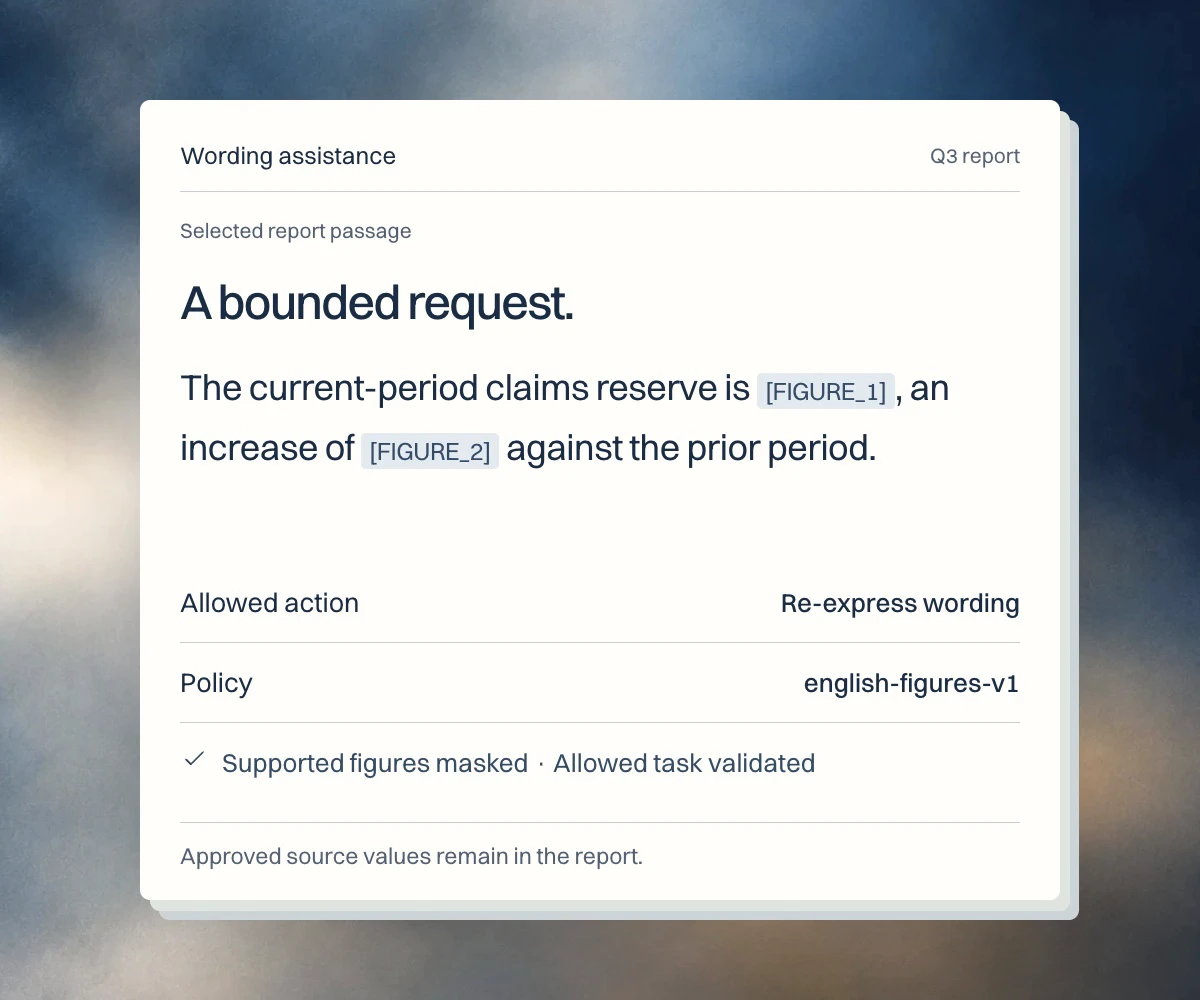
The documented english-figures-v1 policy covers supported numeric and written-number formats. It does not prove that arbitrary prose is free of financial meaning. Other languages and formats need a separately tested policy.
Optional assistance
Keep AI review actions separate from the core reporting process. Confirm the deployment and provider arrangement for your environment.
Use defined mapping suggestions, statement review, and wording assistance. The organisation controls provider configuration and credentials.
Use the reporting workflow without requesting AI review actions. Source tracing, preparation, and checking remain the focus.
Your production environment
Production AI credentials require an organisation-scoped managed secret reference. Development credential fallbacks are not accepted in production.
Access & evidence
Authentication, organisation and team access, reporting roles, and server-side authorisation define the working boundary. Artifact versions and audit events retain what the application saw and what people decided.
Explore review controls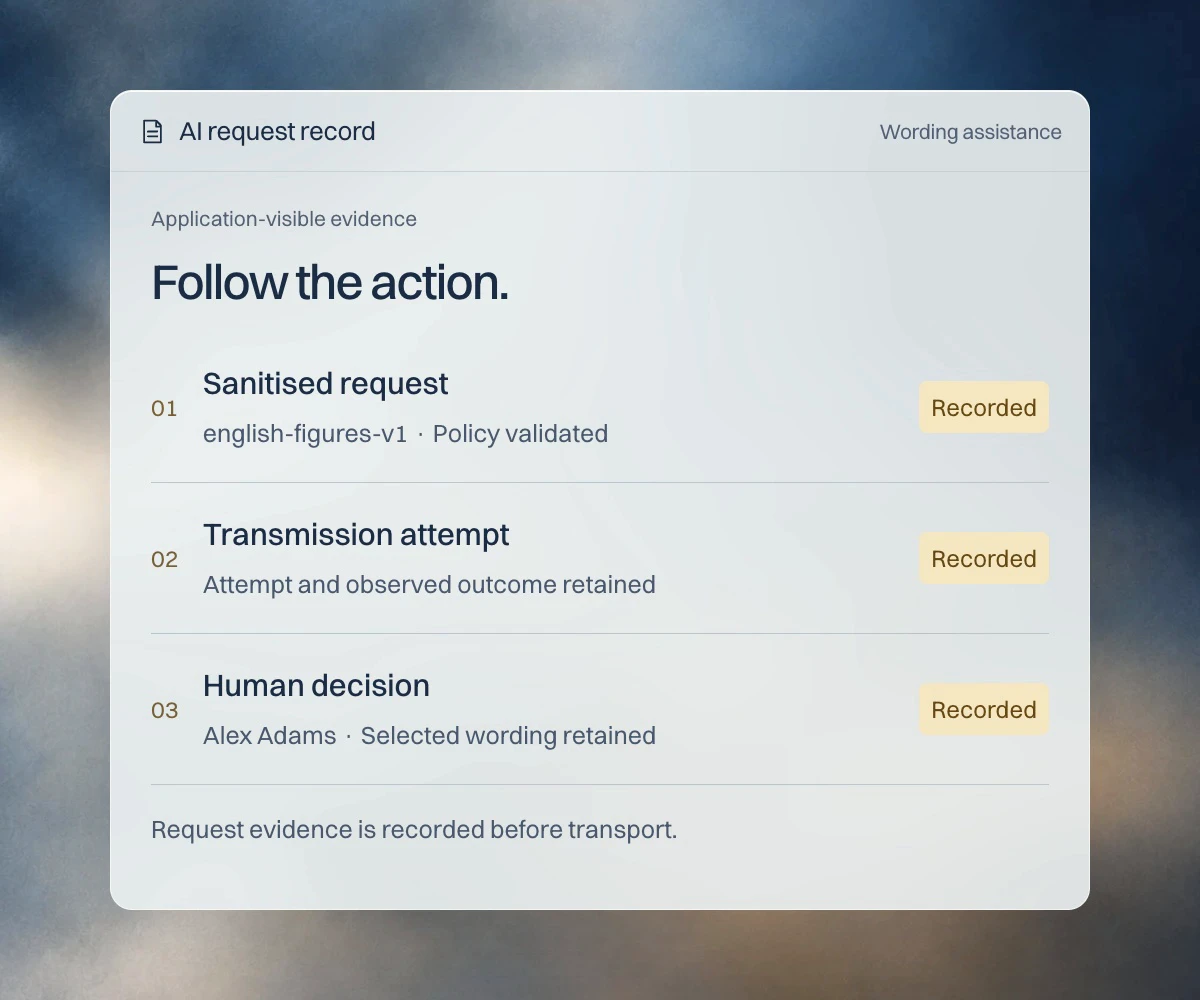
Requests, attempts, responses, validation outcomes, and human decisions. A transmission attempt does not prove provider receipt. Database-only evidence is not tamper-proof against database administrators.
Your governance requirements
Review the control model, deployment requirements, and AI boundaries with your reporting and technology teams.